
SmarterMail Fixes Critical Unauthenticated RCE Flaw with CVSS 9.3 Score
SmarterTools has addressed two more security flaws in SmarterMail email software, including one critical security flaw that could result in arbitrary code execution. The vulnerability, tracked as CVE-2026-24423, carries a CVSS score of 9.3 out of 10.0. "SmarterTools SmarterMail v

Badges, Bytes and Blackmail
Behind the scenes of law enforcement in cyber: what do we know about caught cybercriminals? What brought them in, where do they come from and what was their function in the crimescape? Introduction: One view on the scattered fight against cybercrime The growing sophistication an

OpenClaw Bug Enables One-Click Remote Code Execution via Malicious Link
A high-severity security flaw has been disclosed in OpenClaw (formerly referred to as Clawdbot and Moltbot) that could allow remote code execution (RCE) through a crafted malicious link. The issue, which is tracked as CVE-2026-25253 (CVSS score: 8.8), has been addressed in versio
Privileged File System Vulnerability Present in a SCADA System
We detail our discovery of CVE-2025-0921. This privileged file system flaw in SCADA system Iconics Suite could lead to a denial-of-service (DoS) attack. The post Privileged File System Vulnerability Present in a SCADA System appeared first on Unit 42.
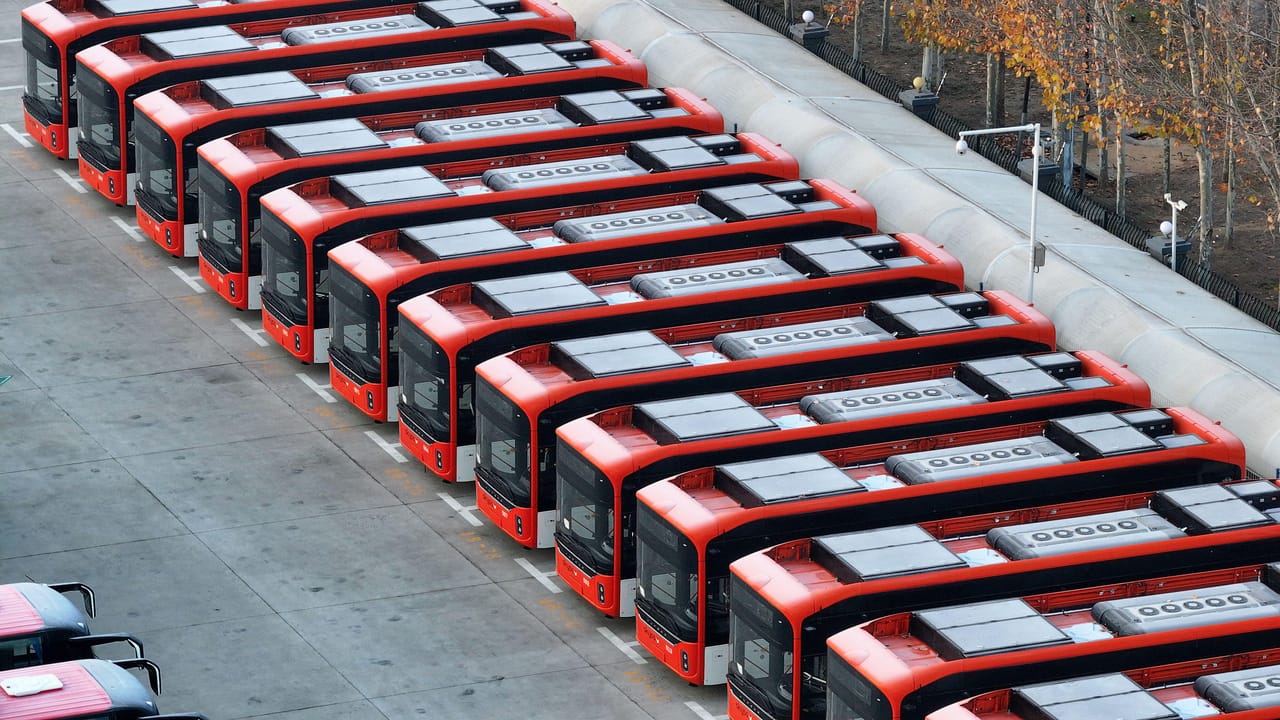
Risky Chinese Electric Buses Spark Aussie Gov't Review
Deployed across Australia and Europe, China's electric buses are vulnerable to cybercriminals and sport remote connectivity some worry the Chinese state could exploit.
Exploited Zero-Day Flaw in Cisco UC Could Affect Millions
Mass scanning is underway for CVE-2026-20045, which Cisco tagged as critical because successful exploitation could lead to a complete system takeover.
Swipe, Plug-in, Pwned: Researchers Find New Ways to Hack Vehicles
Security researchers exploited dozens of vulnerabilities in vehicle infotainment systems and EV chargers during the latest Pwn2Own contest at Automotive World 2026.

Microsoft Rushes Emergency Patch for Office Zero-Day
To exploit the vulnerability, an attacker would need either system access or be able to convince a user to open a malicious Office file.

ThreatsDay Bulletin: Pixel Zero-Click, Redis RCE, China C2s, RAT Ads, Crypto Scams & 15+ Stories
Most of this week’s threats didn’t rely on new tricks. They relied on familiar systems behaving exactly as designed, just in the wrong hands. Ordinary files, routine services, and trusted workflows were enough to open doors without forcing them. What stands out is how little fric

Critical GNU InetUtils telnetd Flaw Lets Attackers Bypass Login and Gain Root Access
A critical security flaw has been disclosed in the GNU InetUtils telnet daemon (telnetd) that went unnoticed for nearly 11 years. The vulnerability, tracked as CVE-2026-24061, is rated 9.8 out of 10.0 on the CVSS scoring system. It affects all versions of GNU InetUtils from versi

Fortinet Confirms Active FortiCloud SSO Bypass on Fully Patched FortiGate Firewalls
Fortinet has officially confirmed that it's working to completely plug a FortiCloud SSO authentication bypass vulnerability following reports of fresh exploitation activity on fully-patched firewalls. "In the last 24 hours, we have identified a number of cases where the exploit w

CISA Updates KEV Catalog with Four Actively Exploited Software Vulnerabilities
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added four security flaws to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation in the wild. The list of vulnerabilities is as follows - CVE-2025-68645 (CVSS score