Supply Chain Attack Secretly Installs OpenClaw for Cline Users
The malicious version of Cline's npm package — 2.3.0 — was downloaded more than 4,000 times before it was removed.

Emerging Chiplet Designs Spark Fresh Cybersecurity Challenges
As scaled-down circuits with limited functions redefine computing for AI systems and autonomous vehicles, their flexibility demands new approaches to safeguard critical infrastructure.
Lessons From AI Hacking: Every Model, Every Layer Is Risky
After two years of finding flaws in AI infrastructure, two Wiz researchers advise security pros to worry less about prompt injection and more about vulnerabilities.
Enigma Cipher Device Still Holds Secrets for Cyber Pros
The Nazi relic's history is riddled with resilience errors, and those lessons still apply to defending against modern cyber threats.
More Than Dashboards: AI Decisions Must Be Provable
AI systems have to be able to show a record of what happened and how.
Spitting Cash: ATM Jackpotting Attacks Surged in 2025
The attacks cost banks more than $20 million in losses last year, as criminals used many of the same tools and tactics they have wielded for more than a decade.
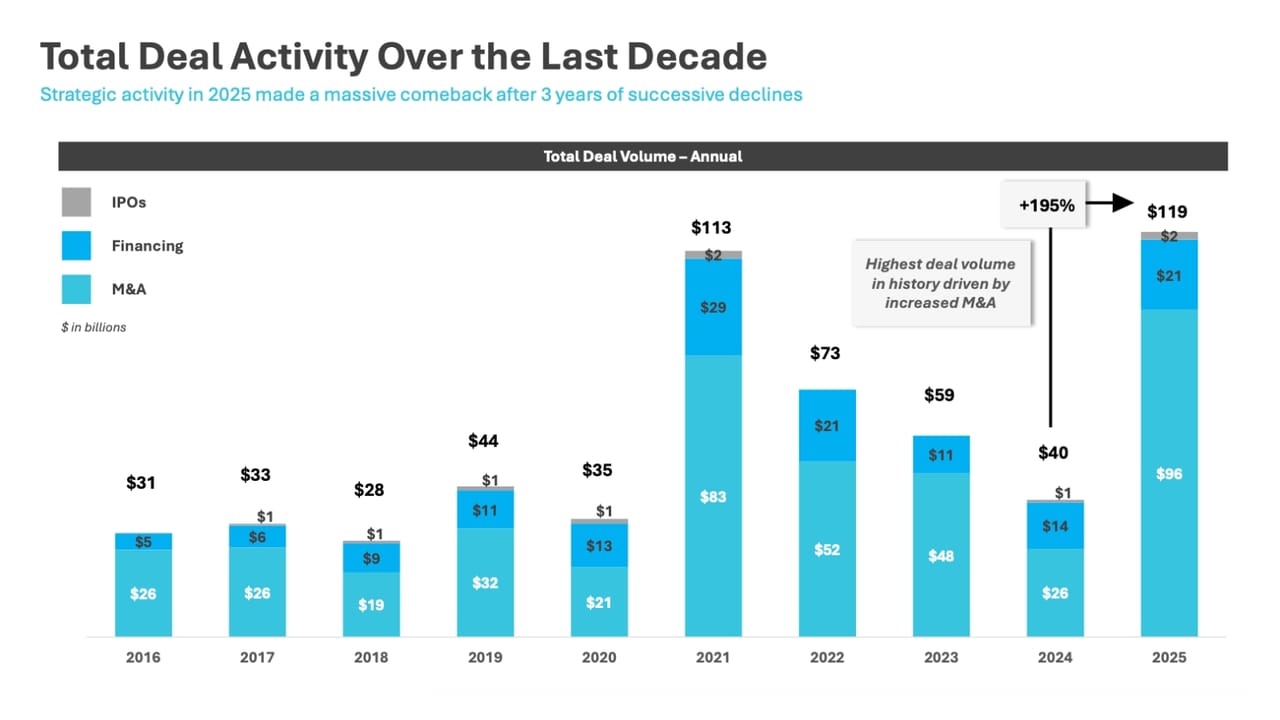
As Cybersecurity Firms Chase AI, VC Market Skyrockets
Investments in cybersecurity startups took off in 2025 as venture capital firms focused not just on AI-native tech but on talent as well.

'Richter Scale' Model Measures Magnitude of OT Cyber Incidents
ICS/OT experts have devised a scoring system for rating the severity and effects of cybersecurity events in operational technology environments.
Why 'Call This Number' TOAD Emails Beat Gateways
Attackers are bypassing email gateways through telephone-oriented attack delivery (TOAD), in which the only email payload is a phone number.
PCI Council Says Threats to Payments Systems Are Speeding Up
The PCI Security Standards Council experienced a record year in many regards, but its first annual report shows it needs to work even faster to stay ahead of attackers.
Flaws in Claude Code Put Developers' Machines at Risk
The vulnerabilities highlight a big drawback to integrating AI into software development workflows and the potential impact on supply chains.
Claude Code Security Shows Promise, Not Perfection
Claude Code's introduction rippled across the stock market, but researchers and analysts say its impact was overstated, as they peel back the layers.